
Face up to new responsibilities
Steph Innes takes a deep dive into the legal framework behind the use of facial recognition technology for retailers
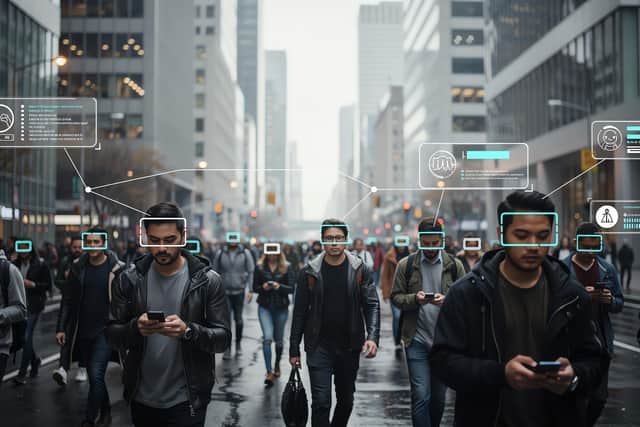
Recent reporting on retailers' use of facial recognition technology (FRT) to address shoplifting has brought a familiar set of questions back into focus. Guidance from the Information Commissioner's Office (ICO) provides a useful indication of how retailers are expected to approach the issue.
In the ICO's eyes, the availability of an FRT solution does not, alone, justify its use. FRT systems typically process biometric data which, when used for identification purposes, constitutes special category personal data under UK data protection law and therefore engages additional legal requirements.
Broadly, these legal requirements mean organisations must demonstrate: why FRT is required; what less intrusive alternatives have been considered; and why they would not achieve the same objective.

This means Data Protection Impact Assessments (DPIAs) are required for many FRT projects - and these should be genuine decision-making tools rather than documents completed post-implementation. If concerns around necessity or proportionality cannot be addressed, organisations should be prepared to reconsider whether FRT is an appropriate solution at all.
That said, FRT extends beyond privacy law – considerations arise in employment law, contracts, procurement requirements and potential disputes arising from its use. Retailers considering FRT for loss prevention must also consider governance, reputational risk and how FRT will operate in practice.
A false identification may create privacy concerns, but could also result in an individual being challenged by security staff, refused entry or subjected to unnecessary investigation. Those outcomes raise wider questions about staff training, escalation procedures, operational decision-making and organisational accountability.
FRT therefore sits at the intersection of multiple legal and operational disciplines: organisations must ensure that its use is justifiable and effectively governed throughout its lifecycle.
In terms of practical steps, ICO guidance also sheds some light on the need for meaningful human review when FRT is deployed. Specifically, the existence of a reviewer does not necessarily equate to meaningful review. Human involvement should amount to more than simply confirming a system-generated alert and reviewers should have sufficient information, authority and training to assess the outcome independently, question it where appropriate and override it where required.
Therefore, retailers looking to implement FRT should build legal, privacy and risk considerations into the project from the outset. They should use DPIAs as decision-making tools assessing necessity, proportionately and less intrusive alternatives, based on testing the system in its intended environment. Robust controls, including watchlists, retention periods, escalation procedures, accountability and meaningful human review should be implemented. Ultimately organisations should adopt a multidisciplinary approach, considering legal, privacy, technology, procurement and employment issues from the outset.
Organisations operating internationally should also be mindful that the regulatory landscape continues to evolve. While the ICO's guidance is grounded in UK data protection law, other legislation such as the EU AI Act points to a broader regulatory focus on biometric technologies, meaning multinational organisations likely need to navigate different rules.
Looking ahead, the overall message is one of accountability. Retailers should be able to demonstrate that FRT deployment has been properly assessed (including through DPIAs), documented and kept under review. As FRT becomes more capable and prevalent, organisations should expect increasing scrutiny not only of how these systems perform, but of the decisions underpinning their use.
This article was co-written by Steph Innes, Partner and Martha Pownall, Associate, Dentons