
Can you afford not to have a cyber insurance policy?
Cyber attacks cost Scottish businesses £386m annually – but most firms still aren’t insured, warns Scott McLuskey
Recent high-profile cyber incidents involving major UK institutions including Marks & Spencer, Harrods, and the Co-op are a stark reminder: no business is immune to attack.

I first spoke about the importance of cyber insurance at the inaugural Cyber Scotland Week six years ago, an initiative supported by the Government to promote cyber resilience. Since then, the threat has only accelerated – today, a cyber-attack occurs every 44 seconds in the UK.
Yet despite the scale of risk, many business leaders remain confident that their organisations are protected. Antivirus software, cloud backups, an in-house or outsourced IT Manager and a general belief that they’re “covered” often mask the reality: these measures alone are not enough.
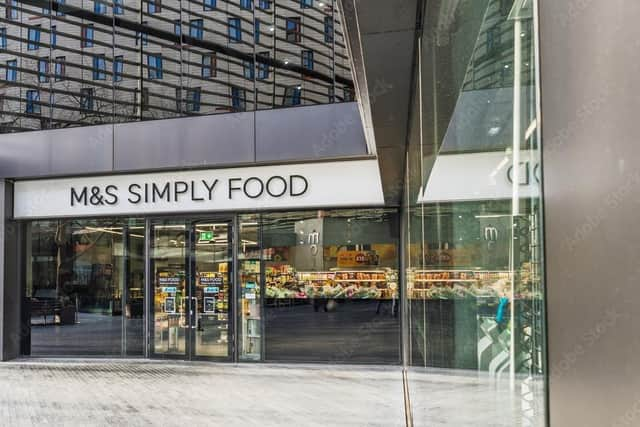
Reports surrounding the recent attack on British retail heavyweight M&S suggest that the attack will cost an estimated £300 million and was not the result of poor systems, but of human error – a tale as old as time and the weakest link in any cyber defence strategy.
Smaller businesses are also firmly in the firing line. Vodafone estimates Scottish SMEs are losing a combined £386m a year to Cyber Attacks, with 40% of SMEs falling victim last year alone. Costs following an attack can be significant: from forensic investigations, legal advice, regulatory notifications, and PR management, to lost revenue, extortion demands, credit monitoring, and potential lawsuits.
The good news is that a cyber insurance policy offers a risk transfer solution to address these costs and assist recovery. Today’s leading cyber policies also go beyond simple risk transfer – they include value-added services like vulnerability scans, penetration testing, and employee training. While not a substitute for a dedicated cybersecurity provider, these tools provide vital early protection and peace of mind.
However, buying cyber insurance isn’t always straightforward. With over 30 readily available cyber insurers – plus Lloyd’s of London – and each provider offering a different proposition with their own minimum cyber security based acceptance criteria, the market can feel impenetrable.
Unlike traditional insurance policies, cyber cover is still relatively new, with the first policy written in the late 1990s - the market and crucially insurer’s loss data is continually developing. Compare that with buildings insurance, first developed in the wake of the Great Fire of London in the 17th century.
As a result, there’s wide variation in policy coverage, pricing, and – most importantly – what policyholders need to do to ensure claims are valid. Too often, businesses only realise this after a breach, when it’s too late.
There are promising signs. Leading providers like CFC Underwriting report a claims payout rate of over 99% and industry-wide improvements are being made in clarity, claims handling, and support services. But challenges remain – particularly for small and medium-sized businesses.
A UK Government report found that 50% of businesses suffered some form of breach in the past year, rising to 70% among medium-sized firms. Yet just over half of all companies have cyber cover.
Scotland’s economy, built on a vibrant mix of SMEs, family-run firms, and fast-growing tech businesses, is particularly exposed. As the majority of organisations have digitised operations, even modest breaches can have a disproportionate impact – not only on individual companies, but on supply chains, customer trust, and investor confidence across the sector. Cyber resilience is no longer just a technical issue; it’s an economic imperative.
The Association of British Insurers has also identified a communication gap: cyber insurance is too often presented as a standalone “product,” when in reality it’s an ongoing service that begins before a breach and supports the business throughout.
At Monteith, we’re working to bridge this gap. We help clients understand their cyber exposure, decode policy language, and choose the right level of cover. Most importantly, we walk our clients through the fine print – ensuring they know exactly what’s required to stay compliant, so their insurance delivers when it matters most.
The threat isn’t going away. Business leaders must go beyond firewalls and backups. They need to take proactive steps – including securing expert cyber insurance advice – to protect against what is now one of the most persistent and costly risks in modern business.
Scott McLuskey is the founder of Glasgow & London based insurance brokerage Monteith
Comments
Want to join the conversation? Please or to comment on this article.